Prioritize Audit Evidence: Policy Management Software for HR
Choose a policy management platform that centralizes the full policy lifecycle, automates attestations and audit evidence, and integrates with your identity and HR systems. Those three capabilities separate a genuine governance tool from a glorified document folder. Screen every vendor on audit evidence quality, automation depth, and integration breadth before you look at anything else, including price.
TL;DR:
- A robust policy management platform must automate the full policy lifecycle, including authoring, approval, distribution, attestation, and retirement, with audit-ready records at each stage.
- Key features to evaluate include role-based approval workflows, immutable audit trails, attestation reminders, policy-to-control mapping, and strong security certifications like SOC 2 and ISO 27001.
- Integration with HRIS and payroll systems is critical to ensure attestation data reflects current employment status, avoiding manual cross-referencing and compliance exposure.
- IT security checks such as SSO compatibility, SCIM provisioning, and API access are essential before signing any vendor contract.
- Pricing varies based on the number of users, policies, and integrations, making detailed planning and pilot testing crucial for a successful rollout.
Table of Contents
- What Policy Management Software Actually Does
- The Feature Checklist That Actually Predicts Vendor Fit
- A Technical Checklist for IT and Security Teams
- Turning Policy Software Into Audit-Ready Evidence
- Budgeting, Timelines, and Where Rollouts Go Wrong
- Why HR and Payroll Data Belongs in Your Audit Evidence
- Editorial Perspective: Audit Defensibility Beats Feature Parity
- Sources
- FAQ
What Policy Management Software Actually Does
Policy management software runs the internal lifecycle of your policies from creation to retirement: author, approve, distribute, attest, and retire. Every stage generates a record, and those records are what an auditor eventually asks to see.
That distinction matters because two other software categories get confused with it constantly. Contract lifecycle management (CLM) tools handle external legal agreements, vendor contracts, and negotiations, not internal governance documents, so a CLM platform will never produce the employee attestation logs a compliance audit requires. Insurance policy administration systems (PAS) manage insurance policies, premiums, and claims, a completely different function that shares only the word “policy” with what you need for internal governance, and confusing the two leads some buyers to purchase products unsuited to their needs](https://www.britecore.com/resources/policy-management-vs-agency-management-understanding-the-difference—-and-why-it-matters).
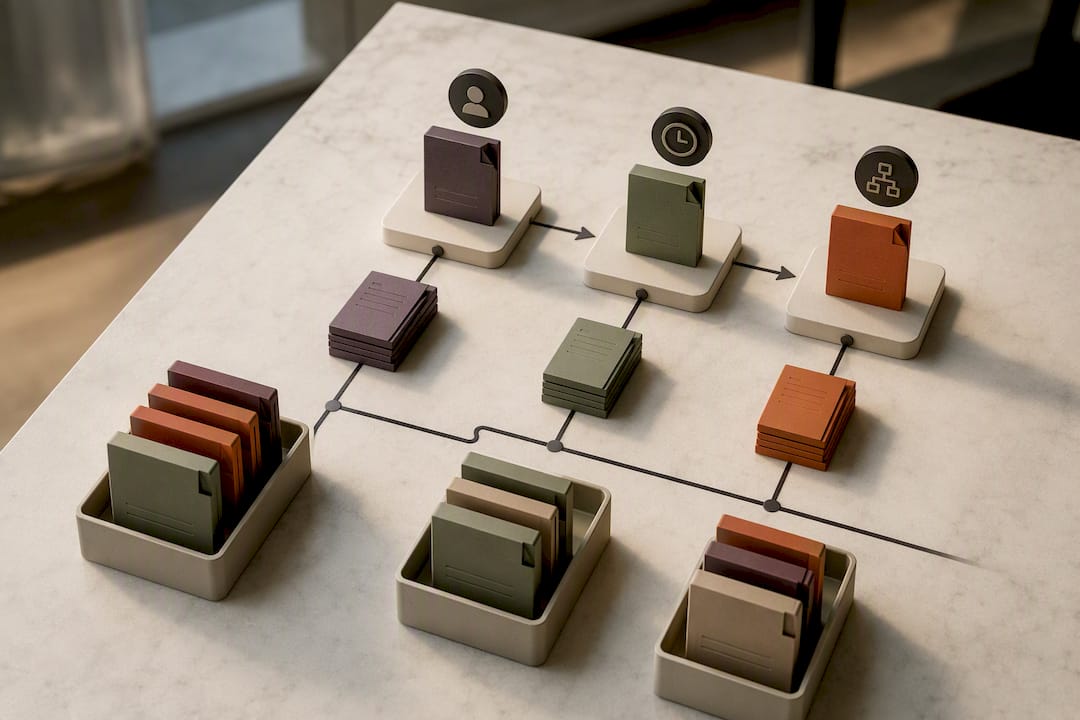
The lifecycle a real policy management tool should automate includes:
- Authoring: templated policy creation with version control from the first draft
- Approval routing: role-based sign-off chains that match your org chart
- Distribution: automatic delivery to the right employee groups
- Attestation: tracked acknowledgment with timestamps
- Retirement: archiving with a preserved audit history
Onspring reports organizations save as much as 70% of the time they’d otherwise spend chasing signatures and updating spreadsheets manually, once that lifecycle runs on automation instead of email threads.
The Feature Checklist That Actually Predicts Vendor Fit
Feature lists in vendor sales decks tend to blur together after the third demo. Score against this checklist instead, and weight the items differently depending on how regulated your organization is.
Core lifecycle features you should see working live in a demo, not described in a slide:
- Editable templates with locked formatting for regulated language
- Role-based approval workflows that mirror your actual org structure
- Full version history with redline comparison between drafts
- Attestation tracking with automatic reminders for non-responders
- Exception management for employees who need a documented waiver
Audit and reporting capabilities deserve extra scrutiny. Ask specifically whether the audit trail is immutable, whether it exports to PDF and CSV formats auditors actually accept, and whether the platform maps individual policies to control frameworks like SOC 2 and ISO 27001. Experts increasingly agree that policy-to-control mapping and automated attestations matter more than any other single feature, because they’re what eliminates the manual document chase during an audit.
Automation and AI capabilities now show up in nearly every serious vendor’s pitch. AI-assisted drafting can flag outdated language against current regulations, and automated notification engines chase down stragglers on attestations without a human sending a single reminder email — see this practical guide to AI w biurze rachunkowym for implementation insights.
Security certifications to request in writing, not just verbally confirmed: SOC 2 Type II reports and ISO 27001 certification. Don’t accept “we’re working toward it.”
Integration needs: single sign-on, HRIS sync, learning management system connections, document storage, and open APIs.
Pro Tip: When you build your scoring matrix, give audit evidence and integrations double the weight of cosmetic features like themes or dashboard color schemes. A regulated organization gets far more value from a clean SOC 2 mapping than from a prettier interface.
A Technical Checklist for IT and Security Teams
Compliance teams pick the shortlist, but IT signs off on the technical fit. Run these checks before any contract gets signed.
- Test SSO during the demo, not after purchase. Confirm SAML or OIDC support and walk through an actual login flow with your identity provider.
- Verify SCIM provisioning so new hires and terminations sync automatically between your HRIS and the policy platform, closing the gap where departed employees still show up as “pending attestation.”
- Map the integration points your organization actually needs: HRIS and payroll systems, document repositories, and ticketing tools for exception handling.
- Confirm API and webhook access exists beyond the sales pitch. Ask for API documentation, not a promise that it’s “on the roadmap.”
- Check export formats for audit evidence. Your GRC platform or SIEM tool needs to ingest attestation logs and policy-to-control mappings without a manual reformatting step.
- Get encryption standards in writing. Data at rest and in transit should meet current industry encryption standards, and the vendor should hand you the SOC 2 or ISO 27001 report on request, not a marketing summary of it.
Turning Policy Software Into Audit-Ready Evidence
Mapping policies directly to controls shortens the single most painful part of any audit: the back-and-forth where an auditor asks for proof and someone spends three days hunting through shared drives. When each policy links to a named control, that link itself becomes the evidence.
The artifacts a well-configured platform should produce on demand include:
- Policy-to-control links tied to named frameworks (SOC 2, ISO 27001, HIPAA)
- Attestation logs with timestamps and named owners
- Full version histories showing who changed what and when
- Owner assignments for every active policy
- Exportable audit appendices formatted for direct auditor consumption
Modern platforms increasingly use AI to surface mapping gaps automatically and generate remediation tasks the moment a policy falls out of sync with its assigned control. That’s a meaningful shift from the older model, where someone on the compliance team had to notice the gap manually, often only when an auditor pointed it out first.
The real test of a platform isn’t whether it holds a library of documents. It’s whether it produces exportable, time-stamped attestations and policy-to-control links an auditor can consume directly, without a human translating the output first.
Budgeting, Timelines, and Where Rollouts Go Wrong
Pricing across this category generally follows one of three shapes: per-user, per-module, or per-employee, and the total cost swings heavily based on how many integrations you need, how many active policies you’re managing, and how deep your reporting requirements go. Probe every one of those cost drivers during the sales call, not after you’ve signed.
Implementation typically takes a few weeks to a few months depending on the number of policies migrated and integrations configured. A successful rollout usually needs a named project owner, IT support for SSO and HRIS connections, and buy-in from department heads who’ll own individual policies going forward.
The most common failure mode is treating the platform as a static repository rather than a living system. Rollouts stall when organizations skip assigning named policy owners and role-based permissions, leaving nobody accountable for updates once the initial migration excitement fades.
Concrete mitigations that consistently work:
- Run a pilot on one high-risk policy domain before attempting an enterprise-wide rollout
- Build an ownership matrix (a RACI chart) before migrating a single document
- Set automated review cadences so policies get revisited on a schedule, not only when an audit forces the issue
- Budget training time for employees who’ll be attesting to policies, not just for the administrators configuring the system
Pro Tip: Pilot with your highest-risk policy domain first, whether that’s data security or workplace safety. Proving value there gets you the internal political capital to expand the rollout without a fight over budget.
Why HR and Payroll Data Belongs in Your Audit Evidence
Attestation logs only tell half the story if they’re disconnected from your actual workforce data. When a policy platform pulls directly from payroll and HR records, it can confirm that every current employee, and only current employees, has a valid attestation on file, without someone manually cross-referencing two systems every quarter.
Some providers work with cannabis operators and other high-risk employers where this gap causes real exposure: a terminated employee still showing an “active” attestation, or a new hire who never got the safety policy because HR and compliance data lived in separate systems. Closing that gap through payroll/HR integration is exactly why zero late filings and audit-ready records have become defining outcomes for clients using an Employer of Record model that keeps compliance and payroll data in sync.
When you’re evaluating vendors on this specific point, ask:
- Does the platform sync automatically with our HRIS on hire and termination dates?
- Can attestation records export in a format our payroll provider can ingest?
- How quickly does a termination in HR reflect in the policy platform’s active-user list?
- Does the integration support multi-state or multi-entity payroll structures?
- What happens to attestation history when an employee changes roles or locations?
- Can the vendor produce a combined HR and policy audit trail in one export?
Editorial Perspective: Audit Defensibility Beats Feature Parity
Most buying guides treat policy management software as a features race: whoever has the longest checklist wins. That’s backwards. The research consistently points to a narrower truth: audit evidence quality and HR/payroll integration predict success far better than feature count does.
Here’s where conventional advice falls short. It treats “attestation tracking” as a checkbox rather than asking whether that attestation data reconciles against a live, current employee roster. A platform can track attestations flawlessly and still produce garbage evidence if it doesn’t know an employee left the company two months ago. Roll With Paid’s work with high-risk, regulated employers makes this gap obvious fast: the moment payroll, HR, and policy data live in separate systems, someone has to reconcile them by hand, and manual reconciliation is exactly where audit findings originate.
Prioritize integration depth over interface polish. Ask harder questions about HRIS sync than about dashboard design. A platform with fewer bells and whistles but airtight, auditor-ready evidence exports will outperform a feature-rich tool that leaves your compliance team cross-referencing spreadsheets every quarter.
— Leah
Sources
For deeper reading beyond this guide, Onspring’s policy management page breaks down lifecycle automation claims in detail, while Axiom Law’s comparison of CLM and policy management clarifies category boundaries that trip up a lot of first-time buyers. PowerDMS offers a solid look at audit-evidence features, and Compyl’s policy management page covers how AI-driven framework mapping works in practice. For rollout planning specifically for regulated employers, Rollwithpaid’s employer resources cover adjacent compliance operations worth reviewing before you sign a contract.
FAQ
How Much Does Policy Management Software Cost?
Pricing typically follows per-user, per-module, or per-employee models, and total cost depends heavily on how many integrations, policies, and reporting features you need. Get a detailed quote based on your actual headcount and integration list rather than a published starting price.
What Is the Best Management Software for Policy Governance?
The best fit centralizes the policy lifecycle (authoring through retirement), automates attestations with immutable audit trails, and integrates with your HRIS and identity provider. No single platform is universally best; the right one depends on your regulatory framework, headcount, and existing tech stack.
What Is a Policy Management System?
A policy management system centralizes and automates how an organization creates, approves, distributes, and tracks acknowledgment of its internal policies. It differs from a document repository because it generates timestamped, auditable records at every lifecycle stage.
What Is the Best Contract Lifecycle Management Software?
Contract lifecycle management (CLM) software is a separate category from policy management. It’s built for external legal agreements and vendor contracts, not internal governance policies, so evaluate CLM tools against different criteria entirely if that’s your actual need.
Recommended
- I-9 and E-Verify: A Compliance Guide for Cannabis Employers
- Understanding Employer of Record for High-Risk Industries
Roll With Paid. is not a law firm and does not provide legal advice. This article summarizes Minnesota law as of August 2026 and is general information only. Tip arrangements are fact-specific; before changing a policy, consult employment counsel or contact DLI Labor Standards at 651-284-5075.